-
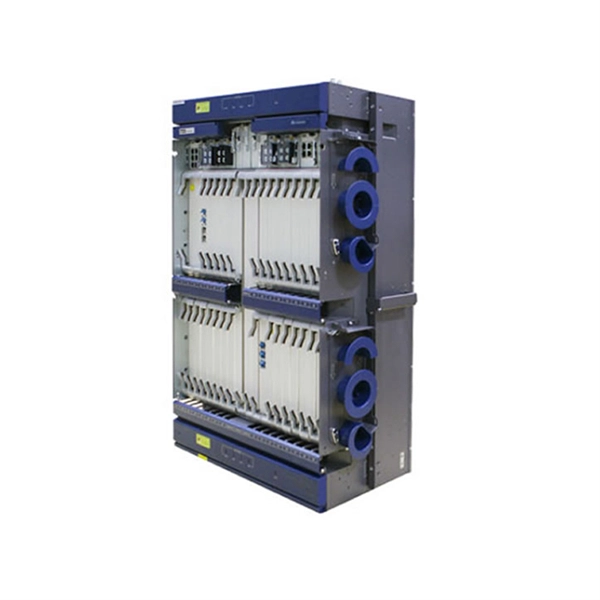
Core Switch Huawei S5700
Huawei S5700 series Ethernet switches are next-generation energy-saving GE switches designed to provide high-bandwidth access and Ethernet multi-service aggregation. Building on next-generation, high-performance hardware and the Huawei Versatile Routing Platform (VRP), the S5700-LI supports Advanced Hibernation Management (AHM). S6700 Series Switches Product Description (V200) S5700 Series Switches Product Description (V200) Huawei CloudEngine S5731-L4P2HT-RUA Remote Unit Switch CloudEngine S6700 Series Switches Product Description (V600) CloudEngine S5700 Series Switches Product Description (V600) CloudEngine S3700 Series. The S5700-LI is a next-generation energy-saving gigabit Ethernet switch that provides flexible GE access ports and 10GE uplink ports. Issue 01 (2019-06-28) Copyright © Huawei Technologies Co.
-
Huawei S7704S Core Switch
The S7700 series provide service optimization features like wired and wireless convergence, unified user management, quality awareness (iPCA), H-QoS, and united security. They provide 100 GE ports, support SVF 2. 0, and have superb scalability and reliability. Uses a fully programmable architecture. The S7700 series switches (S7700 for short) are high-end smart routing switches designed for next-generation enterprise networks. The S7700 design is based on Huawei's intelligent multi-layer switching technology to provide intelligent service optimization methods, such as MPLS VPN, traffic. The S7700 series is available in three models: S7703, S7706, and S7712. System control and management unit for the S7712 and S7706, integrating the control unit, switching unit, and system maintenance unit. Performs concurrent data forwarding using a.
[PDF Version]
-
Huawei Core Switch 3900
S3900 series switches are Gigabit Ethernet access switches with 24 or 48 1G downlink ports and 4 10G uplinks. The switches are ideal for Internet Service Providers (ISPs) and Multiple System Operators (MSOs) to provide home users with triple-play services with up to Gigabit bandwidth. We have 4 HUAWEI Quidway S3900 Series manuals available for free PDF download: Command Manual, Operation Manual, Installation Manual, Specifications Huawei Quidway S3900 Series Pdf User Manuals. With its robust hardware and comprehensive software features, the S3900 Series provides a reliable and scalable solution for a wide range of applications. Page 2 3116A04W Huawei Technologies Co.
-
Core Switch Subnet Configuration
Click the Site Configuration tab, and choose Switch > Subnet in the upper left corner. On the page that appears, click Create. Configure user subnets on the core switch and enable the DHCP relay function on gateway interfaces. Does that mean that on distribution switch, it also needs to be a routed port?In this guide we will be going over how to configure multiple VLANs with routing so that each VLAN has Internet access. When configuring interfaces and routes, you. Review the sections in this module before performing your initial switch configuration tasks that include IP address assignments and DHCP autoconfiguration.
-
Two firewalls are connected to the core switch
Yes, if you add a second core switch, you would need to add a second firewall for redundancy. You can configure the firewalls as active/standby, so when one firewall fails all traffic uses the other firewall. The Core is doing L3 routing for four VFR's. Routes on the Core for all. I have Two Fortigate firewall need to be configured in HA, now my Two LAN cables need to be connected to my single core switch, the firewall will be in Active Passive. Hi, your question is not clear. He put them in as trunk ports with IP addresses on that Juniper switch stack.
-
Enable Telnet on H3C Core Switch
This step-by-step walkthrough will help you: 1️⃣Create VLAN & Assign IP Address 2️⃣Enable Telnet & SSH server on H3C switches 3️⃣Create Local user & password 4️⃣Set Authentication Mode 5️⃣Verification #readtech #H3C #Networking #Telnet #SSH #SwitchConfiguration. This step-by-step walkthrough will help you: 1️⃣Create VLAN & Assign IP Address 2️⃣Enable Telnet & SSH server on H3C switches 3️⃣Create Local user & password 4️⃣Set Authentication Mode 5️⃣Verification #readtech #H3C #Networking #Telnet #SSH #SwitchConfiguration. As shown in Figure 1, the AC is a Telnet server. Configure the AC to permit only Telnet packets sourced from 192. On the IPv4. To create a user on an H3C switch, you can perform this operation through a web interface or SSH. The same CLI commands and configuration steps can also be applied to other H3C switch models. To enable Telnet login, you must enable the Telnet server, configure login. In this video, we discussed H3C CloudNet account creation, adding a device, configuring Telnet on the switch, and then accessing the switch from CloudNet.
[PDF Version]
-
Core Switch Firewall Configuration
In this video, I demonstrate how to configure a Fortinet Firewall in a small office network setup using a core switch. You'll learn how to integrate your FortiGate with a Layer 3 switch, assign VLANs, configure IP addressing, create a default route, and build a firewall policy to. The stack is connected to two Secure Firewalls 3105. The Core is doing L3 routing for four VFR's. Other VFR's are routed on the Firewall. Routes on the Core for all. In this scenario, IP addresses of the interfaces connecting the core switch to the BRASs and firewalls and OSPF need to be configured on the core switch, so as to implement connectivity between the user network to egress network through the core switch. more In this video, we configure OSPF routing between a Core Switch and a Firewall and perform complete. Routing on firewall or core switches? Hello, In my assignment I have to design a network with following components: Configuration: ● Both of the firewalls should be in cluster (HA) ● Both ISP's should be in active-passive mode with dependency with the firewall cluster.
[PDF Version]
-
Does the core switch need its IP address changed
The IP address of the switch can be manually configured or automatically received from a Dynamic Host Configuration Protocol (DHCP) server. If there are no DHCP servers available, the switch will use its factory default IP address which is 192. To remotely manage the device, an IP address must be defined to access the switch. This allows you to easily configure. Unlike routers, which function at Layer 3 and use IP addresses for communication, Layer 2 switches typically do not require an IP address to perform their core tasks. 90 I accessed it this morning by physically plugging in a laptop whose IP I had changed.
-
Restore the core switch
In the CLI, enter boot system config:Factory_Default_Config. There are no specific requirements for this document. The information in this document was tested with these software and hardware versions: Note: Although. This topic can help you reset switch to factory default, please reference following methods (CLI or Web-GUI) to achieve objective. Which situations need this topic: Switch can power on but don't have traffic or forward / switch booting abnormal / function fault. ECS4620 series, ECS4510 series. Resetting or recovering a network switch is a critical task in network maintenance and troubleshooting. Here are the safe methods and pre-reset prep. Every network administrator has faced that moment: a misconfigured switch causing network chaos, or inheriting a device with unknown credentials.
-
Is a 48-port core switch sufficient
A 48-port switch is usually better when port density is already certain, rack space is limited, and lower long-term cost per port matters. In real projects, the most important comparison is often one 48-port switch versus two 24-port switches. From the multitude of models featuring an array of specifications and intended use scenarios, choosing one can quickly become. Both 24-port and 48-port switches serve unique purposes. Below is a comparison of their key features: SMBs, startups, branch offices. Medium to large enterprises, high-density environments. 24 ports, suitable for smaller setups. They're not typically used as core. Choosing the right 48-port network switch is crucial for building a robust and efficient network, whether it's for a growing business, a data center, or a large office setup.
-
OLT uplink or downlink on the core switch
The OLT connects to subscribers over PON. An uplink switch aggregates multiple OLTs and provides the connection to the core network. Switch normal ports, also known as. Downstream traffic is the traffic flowing from an OLT to a specific ONT. Each GEM port is identified by a unique ID called port ID. The GEM ports encapsulate the Ethernet services into GEM frames, add. In network architecture, uplinks serve as the core channels for communication across hierarchical devices. They manage the vertical data aggregation between access layer switches and aggregation or core level devices (such as core switches and routers) within a Local Area Network (LAN). Here is how they differ and when each makes sense.
-
Core Switch Link Technology
Includes dual power supplies, hot-swappable modules, link aggregation (LAG), and support for HSRP/VRRP. Modular chassis or stackable designs make it easy to scale as your network grows. A core switch is a high-performance network switch located at the core layer of the network architecture. It is mainly responsible for high-speed forwarding and management of large amounts of data traffic from various aggregation layer switches. Sitting at the top of the hierarchical model, core switches interconnect distribution layer switches and provide high-speed data transfer across. Core switches are the focal point for traffic control between access and distribution switches. Scalability: They can handle a italic large number of connections italic and adapt to growing network demands. Redundancy: Many core switch.
-
Botswana Core Switch 100G
Enterprise SONiC based 32 port 100G QSFP28 aggregation core switch for aggregation spine architecture, which line rate L2 L3 up to 3. 2Tbps, Marvell Falcon, ROCEv2 EVPN Multi homing supported. FS 100G Switches offer high programmability and scalability, designed for large enterprises and hyper-converged infrastructure (HCI) networks. Learn more!The Wedge 100-32X switch provides 32 QSFP28 ports that can each run at 100GbE/40GbE, or as 4 x 25 GbE/4 x 10 GbE/2 x 50 GbE through breakout cables. Wedge100-32X Warranty Support Period: 3 years. An ultra-fast enterprise switch with extra processing power due to the. Arista Networks is the leader in building software driven cloud networks for today's datacenter, cloud and campus environments. Arista delivers the most efficient, reliable and high performance Universal Cloud Network architectures based on 10G, 25G, 40G, 50G, 100G and 400G platforms delivered with. With the trend of high speed Ethernet, 10/40/100Gbps, Edgecore switches offer a complete set of advanced software features that will easily satisfy the demands of enterprises and SMBs everywhere.
[PDF Version]
-
Core Switch VRP
This chapter describes how to configure the Virtual Router Redundancy Protocol (VRRP) on a switch This chapter includes the following sections: • Information About VRRP • Licensing Requirements for VRRP • Guidelines and Limitations • Default Settings • Configuring VRRP . This chapter describes how to configure the Virtual Router Redundancy Protocol (VRRP) on a switch This chapter includes the following sections: • Information About VRRP • Licensing Requirements for VRRP • Guidelines and Limitations • Default Settings • Configuring VRRP . VRRP is a popular protocol for providing device redundancy, for connecting redundant WAN gateway routers or server access switches. It allows a backup router or switch to automatically take over if the primary (master) router or switch fails. There are only small command differences. Here, you will learn How to. Configure virtual router redundancy protocol (VRRP)_on your device with the steps and examples below. routing-options] hierarchy level. The Virtual Router Redundancy Protocol (VRRP) groups multiple routing devices into a virtual router. "Feature Typical Configuration Examples" provides.
[PDF Version]
-
How large a rack should the core switch be placed in
Rack mounting is the most common method used for housing network switches in data centers and server rooms. Switches are installed on standard 19-inch racks using mounting brackets or rails. This setup offers easy accessibility, efficient cable management, and scalability. Wall mounting is ideal. As mentioned above, you should place the equipment thoughtfully, first of all, because the IT infrastructure in the rack is supposed to work non-stop for a long time, and later you may not be able to make changes in the installation without affecting the performance.
-
Dutch Consulting Core Switch 100G
Enterprise SONiC based 32 port 100G QSFP28 aggregation core switch for aggregation spine architecture, which line rate L2 L3 up to 3. 2Tbps, Marvell Falcon, ROCEv2 EVPN Multi homing supported. The C-LIGHT CLS6862-54XC is a 100G high-performance switch designed for data centers and enterprise networks, delivering robust performance, reliability, and scalability. Features ●Powerful Forwarding Capability -1. Especially for companies with many locations and very high data traffic, the 32 high-performance 100G wire-speed QSFP28 industry-standard ports. FS 100G Switches offer high programmability and scalability, designed for large enterprises and hyper-converged infrastructure (HCI) networks. FS 100 Gigabit data centre switches with build-in broadcom switch chip provides powerful hardware switching capacity and data centre features (supporting stacking, MLAG, PFC, ECN, VxLAN, EVPN, REUP, etc), making them ideal for cloud data centre and high-end campus network.
[PDF Version]